OpenSnitch Download Guide for Linux Systems in 2026 is essential for users who want advanced outbound firewall protection and complete control over application internet access on Linux devices. As cybersecurity threats continue to grow, Linux users are increasingly adopting interactive firewalls that provide visibility into outgoing connections and suspicious network activities. OpenSnitch has become one of the most trusted open-source solutions for improving privacy and monitoring internet communication in real time.
OpenSnitch offers a user-friendly graphical interface combined with powerful network filtering capabilities. Whether you use Ubuntu, Fedora, Debian, Arch Linux, or another Linux distribution, the tool helps you manage internet permissions application by application. This guide explains everything from downloading and installing OpenSnitch to configuring firewall rules, troubleshooting issues, improving security, and understanding how OpenSnitch works in modern Linux environments.
What Is OpenSnitch?
OpenSnitch is an open-source interactive application firewall designed specifically for Linux operating systems. It allows users to monitor, block, and control outgoing internet connections generated by applications and processes running on the system.
Unlike traditional firewalls that mainly focus on incoming traffic, OpenSnitch specializes in outbound traffic management. Whenever an application attempts to establish a network connection, OpenSnitch immediately notifies the user and asks whether the connection should be allowed or denied.
This approach gives users greater transparency and security because hidden connections, trackers, telemetry services, and potentially malicious activities become visible in real time.
Key Features of OpenSnitch
Interactive Connection Alerts
The software displays pop-up notifications whenever applications attempt internet access. Users can choose to allow or deny the connection temporarily or permanently.
Application-Based Filtering
OpenSnitch creates rules based on individual applications, domains, IP addresses, ports, or protocols.
Real-Time Network Monitoring
Users can monitor active connections, bandwidth usage, and application network behavior from the graphical dashboard.
System-Wide Protection
The firewall protects the entire Linux environment rather than focusing on a single browser or application.
Open-Source Security
Since OpenSnitch is fully open source, developers and security researchers can review the code for transparency and reliability.
Linux Compatibility
The software supports major Linux distributions, including Ubuntu, Debian, Fedora, Arch Linux, Linux Mint, and Manjaro.
Why OpenSnitch Is Important in 2026
Linux systems are becoming increasingly popular among developers, businesses, cybersecurity professionals, and privacy-conscious users. As more applications rely on cloud services and background internet communication, monitoring outbound traffic has become extremely important.
Growing Privacy Concerns
Many modern applications communicate with external servers without user awareness. Some applications collect analytics, telemetry data, or usage statistics. OpenSnitch allows users to identify and block unnecessary connections.
Protection Against Malware
Malware often attempts to connect to remote servers for data theft or command execution. OpenSnitch can immediately detect suspicious outbound activity and prevent unauthorized communication.
Increased Remote Work
Remote workers frequently use Linux systems for development and business operations. Interactive firewall protection improves network security for sensitive workflows.
Better Network Transparency
Users gain complete visibility into which applications access the internet, when they connect, and where they send data.
How OpenSnitch Works
OpenSnitch operates through two major components:
OpenSnitch Daemon
The daemon runs in the background and intercepts outgoing network connections. It communicates with Linux firewall frameworks such as nftables or iptables.
OpenSnitch User Interface
The graphical interface displays alerts, logs, statistics, and firewall management tools.
When an application requests internet access, the daemon sends the request to the GUI. The user then decides whether the connection should be permitted or blocked.
Rule Creation Process
Users can create rules based on:
- Application name
- Domain name
- IP address
- Port number
- Protocol
- Duration
- User session
Rules can be temporary or permanent, depending on user preference.
System Requirements for OpenSnitch
Before downloading OpenSnitch, users should verify system compatibility.
Minimum Requirements
Operating System
- Ubuntu
- Debian
- Fedora
- Arch Linux
- Linux Mint
- Manjaro
- Other compatible Linux distributions
Hardware Requirements
- Dual-core processor
- Minimum 2 GB RAM
- At least 200 MB of free storage
Software Requirements
- Python 3
- Systemd
- nftables or iptables support
- The GTK desktop environment is recommended.
OpenSnitch Download Methods
There are several methods available for downloading OpenSnitch on Linux systems.
Official Package Downloads
Most users download prebuilt packages for their Linux distribution.
Source Code Installation
Advanced users may compile OpenSnitch from source code for custom configurations.
Package Managers
Many Linux distributions allow installation directly from repositories or package managers.
How to Download OpenSnitch on Ubuntu
Ubuntu remains one of the most popular Linux distributions for OpenSnitch users.
Step 1: Update the System
Before installation, update package indexes and system repositories.
sudo apt update && sudo apt upgrade
Step 2: Download OpenSnitch Packages
Users typically download:
- OpenSnitch daemon package
- OpenSnitch graphical interface package
Step 3: Install Dependencies
Ubuntu may require additional dependencies before installation.
sudo apt install python3-pip python3-setuptools
Step 4: Install OpenSnitch
Install the downloaded packages using the package manager.
sudo apt install ./opensnitch*.deb ./python3-opensnitch-ui*.deb
Step 5: Start the Service
Enable and start the daemon service.
sudo systemctl enable --now opensnitch
Step 6: Launch the User Interface
Open the GUI from the application menu.
OpenSnitch Download Guide for Debian
Debian users follow a process similar to Ubuntu.
Repository Preparation
Ensure the system repositories are fully updated.
sudo apt update
Package Installation
Install OpenSnitch packages manually or through compatible repositories.
Service Verification
Verify the daemon status after installation.
systemctl status opensnitch
Installing OpenSnitch on Fedora
Fedora users can install OpenSnitch using RPM packages.
Update Fedora Packages
sudo dnf update
Install Required Libraries
sudo dnf install python3 python3-pip
Install OpenSnitch RPM
sudo rpm -i opensnitch*.rpm
Enable the Service
sudo systemctl enable --now opensnitch
Installing OpenSnitch on Arch Linux
Arch Linux users usually install OpenSnitch through the AUR repository.
Install Git and Base Development Packages
sudo pacman -S git base-devel
Clone the AUR Repository
git clone https://aur.archlinux.org/opensnitch.git
Build and Install
cd opensnitchmakepkg -si
Start the Service
sudo systemctl enable --now opensnitch
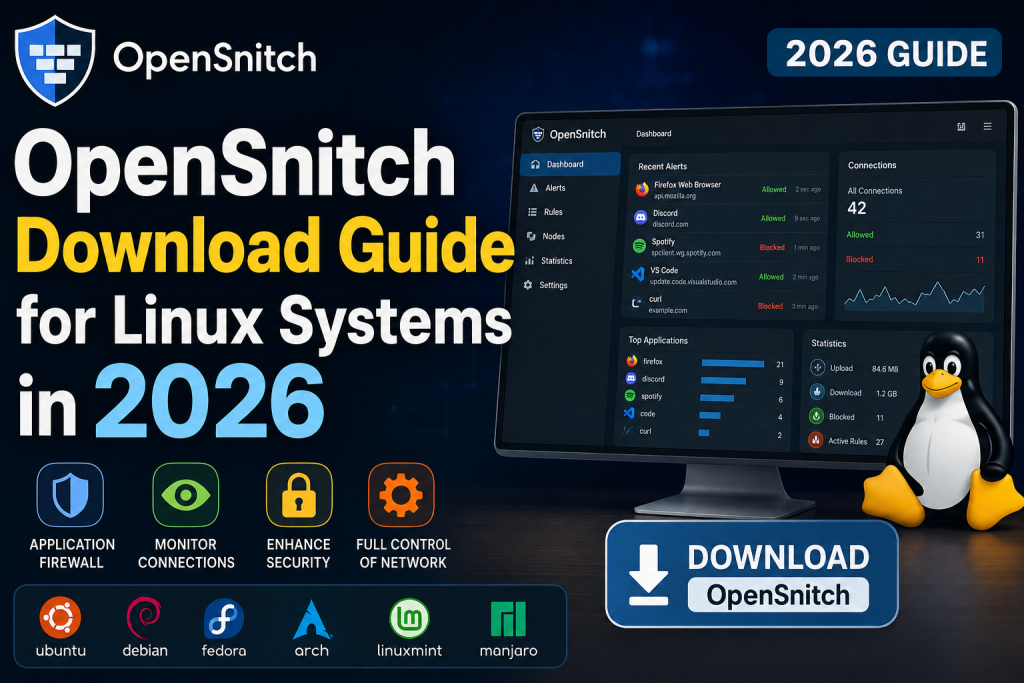
OpenSnitch User Interface Overview
The graphical interface provides centralized firewall management.
Dashboard
The dashboard displays:
- Active connections
- Recent alerts
- Connection statistics
- Firewall rules
- System activity
Nodes Section
The nodes section shows monitored devices and active agents.
Rules Manager
Users can create, edit, delete, and organize firewall rules.
Statistics Panel
Real-time network monitoring helps identify suspicious behavior.
Understanding OpenSnitch Alerts
One of the most important OpenSnitch features is its interactive alert system.
Alert Components
An alert usually contains:
- Application name
- Destination IP
- Domain name
- Protocol
- Port number
- Process ID
Available Actions
Users may:
- Allow connection
- Deny connection
- Create a permanent rule.
- Allow temporarily
- Block temporarily
Rule Scope Options
Rules can apply to:
- Single process
- Entire application
- Domain
- Port
- Session
Best OpenSnitch Configuration Settings
Proper configuration improves usability and security.
Enable Notifications
Notifications help users monitor new outgoing requests immediately.
Create Smart Rules
Avoid excessive prompts by creating intelligent application rules.
Use Domain Filtering
Blocking unnecessary domains improves privacy.
Monitor Unknown Applications
New or suspicious applications should always be reviewed carefully.
Regularly Review Logs
Connection logs help identify unusual behavior.
OpenSnitch Firewall Rules Explained
Firewall rules determine how applications communicate with external networks.
Allow Rules
Allow rules permit outgoing connections.
Deny Rules
Deny rules block specific network activities.
Temporary Rules
Temporary permissions expire after a certain duration.
Permanent Rules
Permanent rules remain active until manually modified.
Wildcard Rules
Advanced users can use patterns for broader filtering.
OpenSnitch vs Traditional Linux Firewalls
OpenSnitch differs significantly from conventional Linux firewall tools.
OpenSnitch
- Outbound traffic focus
- Interactive prompts
- Application-level control
- GUI-based management
UFW
- Port-based filtering
- Simpler firewall management
- Less application visibility
Firewalld
- Zone-based firewall control
- Enterprise networking support
nftables
- Advanced packet filtering
- Command-line focused
Benefits of Using OpenSnitch
Better Privacy
Applications cannot secretly communicate without permission.
Improved Security
Suspicious network behavior becomes visible immediately.
Full User Control
Users decide which applications may access the internet.
Lightweight Performance
OpenSnitch generally consumes minimal system resources.
Educational Value
Users learn how applications interact with networks.
Common OpenSnitch Use Cases
Blocking Telemetry
Prevent applications from sending analytics data.
Restricting Browser Access
Control browser communication with tracking services.
Monitoring Development Tools
Developers can inspect application network behavior.
Detecting Malware
Unexpected outbound connections may indicate compromise.
Protecting Sensitive Systems
Servers and workstations gain additional outbound protection.
OpenSnitch Security Features
Domain Filtering
Users can block unwanted domains globally.
Process Monitoring
The firewall tracks individual application processes.
DNS Monitoring
DNS requests become visible for analysis.
Network Event Logging
All network activity is stored for review.
Real-Time Analysis
Immediate alerts help stop suspicious activity quickly.
Troubleshooting OpenSnitch Installation Issues
Some users may encounter installation problems.
Dependency Errors
Install missing Python packages or libraries.
Service Startup Failures
Check daemon status:
systemctl status opensnitch
GUI Not Launching
Ensure graphical dependencies are installed correctly.
Firewall Conflicts
Disable conflicting firewall applications temporarily.
Permission Problems
Verify sudo privileges and system permissions.
How to Uninstall OpenSnitch
Users can remove OpenSnitch if needed.
Ubuntu and Debian Removal
sudo apt remove opensnitch python3-opensnitch-ui
Fedora Removal
sudo dnf remove opensnitch
Arch Linux Removal
sudo pacman -R opensnitch
OpenSnitch Performance Impact
Many users worry about firewall performance overhead.
CPU Usage
OpenSnitch usually consumes minimal CPU resources.
RAM Consumption
Memory usage remains relatively low for modern systems.
Network Speed
The firewall generally does not reduce internet speed significantly.
Startup Impact
The daemon starts automatically with the operating system.
OpenSnitch for Developers
Developers benefit greatly from OpenSnitch visibility features.
API Monitoring
Inspect which APIs applications access.
Debugging Applications
Identify unexpected network requests during development.
Secure Testing Environments
Restrict outbound communication in testing systems.
Privacy Auditing
Verify whether applications leak unnecessary data.
OpenSnitch for Cybersecurity Professionals
Security experts often use OpenSnitch for monitoring and incident response.
Threat Detection
Outbound traffic analysis helps detect compromise indicators.
Malware Investigation
Researchers can observe malware communication attempts.
Network Behavior Analysis
Suspicious application behavior becomes easier to identify.
Security Hardening
OpenSnitch adds another defensive layer to Linux systems.
OpenSnitch Logging and Analytics
Logs provide detailed insight into network behavior.
Connection History
Review previous outbound requests.
Application Statistics
Track bandwidth and usage patterns.
Exporting Logs
Advanced users may export logs for external analysis.
Monitoring Trends
Repeated requests can indicate automated behavior.
OpenSnitch Privacy Advantages
Privacy-conscious users increasingly rely on outbound filtering.
Blocking Tracking Services
Applications often communicate with tracking servers silently.
Reducing Data Collection
Users control what information leaves the system.
Improved Transparency
Every outgoing request becomes visible.
Limiting Background Communication
Unused applications can be prevented from connecting online.
OpenSnitch and Modern Linux Desktops
OpenSnitch integrates well with desktop Linux environments.
GNOME Compatibility
The interface works smoothly with GNOME desktops.
KDE Plasma Support
KDE users can manage OpenSnitch effectively.
XFCE and Lightweight Environments
Even lightweight Linux desktops support OpenSnitch.
OpenSnitch Alternatives in 2026
Several alternatives exist for Linux firewall management.
Portmaster
A privacy-focused network monitoring application.
GUFW
A graphical interface for UFW.
Firewalld
Enterprise-grade firewall management.
iptables
Traditional Linux firewall framework.
nftables
Modern packet filtering system.
Common Mistakes New Users Make
Allowing Everything Automatically
Blindly approving requests defeats firewall security benefits.
Ignoring Alerts
Important security warnings should never be dismissed casually.
Creating Overly Broad Rules
Broad permissions reduce system security.
Forgetting to Review Logs
Logs provide valuable security insights.
Tips for Using OpenSnitch Efficiently
Start with Learning Mode
Observe application behavior before creating permanent rules.
Block Unknown Connections
Unrecognized processes should be investigated carefully.
Organize Rules Properly
Structured rules simplify firewall management.
Update OpenSnitch Regularly
New versions improve compatibility and security.
Backup Configuration Files
Saving rules prevent data loss during reinstalls.
Future of OpenSnitch
OpenSnitch continues evolving as Linux security needs grow.
Improved Interface Design
Future updates may introduce better usability features.
Enhanced Rule Management
More intelligent automation is expected.
Better Wayland Support
Modern Linux display servers will receive improved compatibility.
Expanded Monitoring Features
Advanced analytics and visualization tools may appear.
Why Linux Users Prefer OpenSnitch
Linux users value transparency, privacy, and control.
Open-Source Philosophy
The community trusts transparent software.
Granular Permissions
Users gain detailed control over network communication.
Community Development
OpenSnitch benefits from active developer contributions.
Strong Privacy Protection
The firewall reduces unwanted data transmission.
OpenSnitch Best Practices
Use the Principle of Least Privilege
Allow only necessary network access.
Audit Rules Monthly
Regular audits improve long-term security.
Monitor Startup Applications
Startup programs often generate background traffic.
Combine with System Firewall
Use OpenSnitch alongside UFW or nftables for layered security.
Conclusion
OpenSnitch remains one of the most powerful and practical outbound firewalls available for Linux systems in 2026. Its ability to monitor, control, and analyze outgoing connections gives users unmatched visibility into application behavior and network activity. Whether you are concerned about privacy, malware protection, development monitoring, or advanced firewall management, OpenSnitch provides a flexible and reliable solution.
OpenSnitch is especially valuable for users who want full transparency over internet communication on Linux devices. With support for major Linux distributions, real-time alerts, customizable rules, and detailed monitoring capabilities, the software continues to grow as an essential security tool for modern Linux environments. Proper installation, smart configuration, and consistent monitoring can significantly improve both system security and personal privacy.